English
 Ελληνικά
 Mastering the Forex Market: Unleashing the Power of Dedicated Servers for MT5 Hosting
 Dedicated Servers in 2025: Why Businesses Are Moving Back
 NetShop ISP Expands Global Reach with PoP VPS Solution
 MT5 Access Server for Forex Brokers: Virtual vs. Dedicated
 6 Reasons Why Your WordPress Website Is Slow And How to Fix It
 How To Setup DKIM and SPF Records on cPanel (Jupiter theme)
 5 Advantages of Colocation Vs. On Premise Hosting
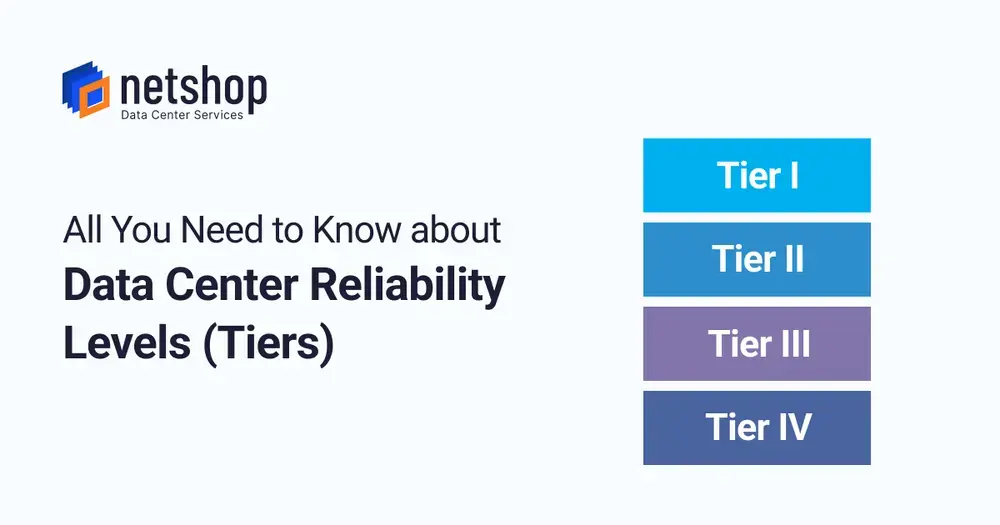 All You Need to Know about Data Center Reliability Levels (Tiers)
 XConnect: Ultra‑Low Latency Connectivity Now Delivered Globally
 Cloud Hosting Trends 2025: Bare Metal, Hybrid Cloud & Web3 Hosting
 Introducing Hybrid & Workload-based Cloud Backup Solutions
 How can Forex Brokers be Protected from DDoS Attacks

This is announcement published by Synacor regarding the zero-day exploit vulnerability for Log4j
After intensive review and testing, Zimbra Development determined that the zero-day exploit vulnerability for Log4j (CVE-2021-44228) does not affect the current supported Zimbra versions 9.0.0 and 8.8.15.
Zimbra Collaboration Server currently uses Log4j version 1.2.16. The cause of the vulnerability is found in the lookup expression feature in Log4j versions 2.0 to 2.17.
Also, the Redhat (CVE-2021-4104) vulnerability does not affect the current Supported Zimbra Collaboration Server versions 9.0.0 and 8.8.15. For this vulnerability to affect the server, it needs JMSAppender and the ability to append configuration files. Zimbra does not use the JMSAppender.
The Zimbra Development team is in the process of upgrading Log4j which is expected to be completed within Q1 2022.
Read more about the Log4j vulnerability and how to protect your organization’s infrastructure.