
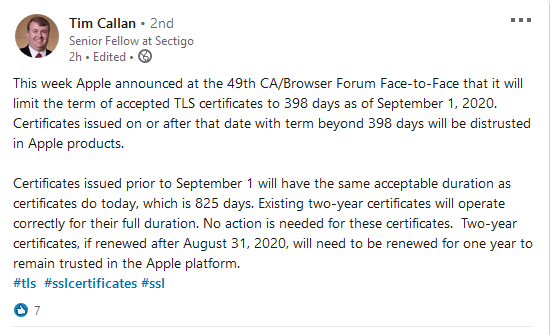
Starting September 1st in 2020, Apple’s Safari browser will no longer trust SSL/TLS leaf certificates with validity of more than 398 days which is the equivalent of a one-year certificate plus the renewal grace period. Other types of SSL/TLS certificates, including intermediates and roots, are unaffected.
At the CA/Browser (CA/B) Forum in Bratislava, Slovakia, this week, Apple announced that beginning Sept. 1, newly issued publicly trusted TLS certificates are valid for no longer than 398 days. This followed a long history of the CA/B Forum community working to reduce certificate lifetimes and improve security, while balancing the needs of business owners in transitioning to shorter validity certificates.
Is Shorter Validity a Good Thing?
We knew it was only a matter of time before this type of initiative would occur. Last year, we wrote on how one-year certificate validity was back on the ballot of the CA/B Forum. The idea here is that the shorter an SSL/TLS leaf certificate’s validity period, the more secure the certificate is.
That’s the argument that’s been made for several years for why browsers wanted to cap the maximum validity for SSL/TLS certificates to 1 year. The theory is that by requiring SSL/TLS certificates to be renewed after a shorter period:
- When any security updates to certificates are made, they roll out into the wild more quickly.
- It also theoretically makes websites more secure by ensuring that new keys are being generated regularly.
What does this mean for certificate users? For your website to be trusted by Safari, you will no longer be able to issue publicly trusted TLS certificates with validities longer than 398 days after Aug. 30, 2020. Any certificates issued before Sept. 1, 2020 will still be valid, regardless of the validity period (up to 825 days). Certificates that are not publicly trusted can still be recognized, up to a maximum validity of 825 days.